Skip to content

Helxis HEDE

One security platform

Helxis HEDE brings every security module onto one platform: from endpoint protection and endpoint detection and response to estate-wide event collection, correlation, extended detection and data protection. One data model, one console, one incident queue — what the endpoint saw is joined here to what the estate saw.

One platform, five modules

Endpoint security, EDR, XDR, DLP and SIEM are not five products competing for one budget. Each name says where a defence sits and which question it answers. Reading them as alternatives is the shortest route to paying twice for one capability and leaving another uncovered entirely.

Endpoint security is the pair that lives on the machine itself. EPP judges files on the machine itself and stops what it finds: a file is checked when it is written and when it is launched, and on Linux the verdict is reached before the process starts. An attack stopped here leaves little damage behind to investigate. EDR assumes something already ran, and keeps the record that can answer what it did — which process started which, what it wrote, where it connected.

The disciplines, and the question each one answers
DisciplineWhat it watchesThe question it answers
EPP — endpoint protectionThe file, when it is written and launchedShould this file be allowed to run?
EDR — detection and responseProcesses, memory and connections on the machineWhat happened on this host, and who started it?
SIEM — event managementLogs from every source in the estateWhat did the whole estate see?
XDR — extended detectionEndpoint, identity and network signals togetherIs this one attack, or separate incidents?
DLP — data loss preventionThe movement of sensitive dataWhere is this data going, and should it be?

HEDE stands for Helxis Endpoint Defense Engine. All five modules are parts of one platform: one data model, one incident queue, one console — so a process on the endpoint and an authentication in the estate meet on the same screen. Modules are enabled per deployment: a customer starts with what they need and adds the rest to that same console, with no second system and no second pane of glass.

SIEM on real screens · EPP on real screens · Prices per module and the calculator are further down

The platform does not replace your defences — it connects them

Every security tool sees only its own event: antivirus sees a file, the firewall a connection, the WAF a request. None of them knows what the others saw. An attack passes exactly between them.

The platform does not replace them — it builds one layer of observation, detection and accounting above them. A single query works across every source, because events are reduced to one model: a field with the same name means the same thing whichever vendor produced it.

So search, correlation rules, dashboards and reports are not tied to a source type. Adding a new vendor does not mean rewriting the rules.

An event's path through the platform
StageWhat happens
IngestSource verified, buffered to disk, duplicates and losses accounted for
ProcessingParsing, normalisation to the single model, categorisation, enrichment with context
DetectionCorrelation rules, behavioural profiles, alerts raised
PresentationIncidents, dashboards, reports and forwarding to external systems
Platform capabilities

What It Is Made Of

Data collection

  • 13 ingest methods: Syslog (UDP/TCP/TLS), agent, REST API, WMI, SNMP, files, databases, queues, clouds, NetFlow
  • 600+ source types with ready parsing rules in the base distribution
  • Agent and agentless: a network method wherever an agent cannot be installed
  • Your own decoder is written as configuration — without touching product code

SIEM at work

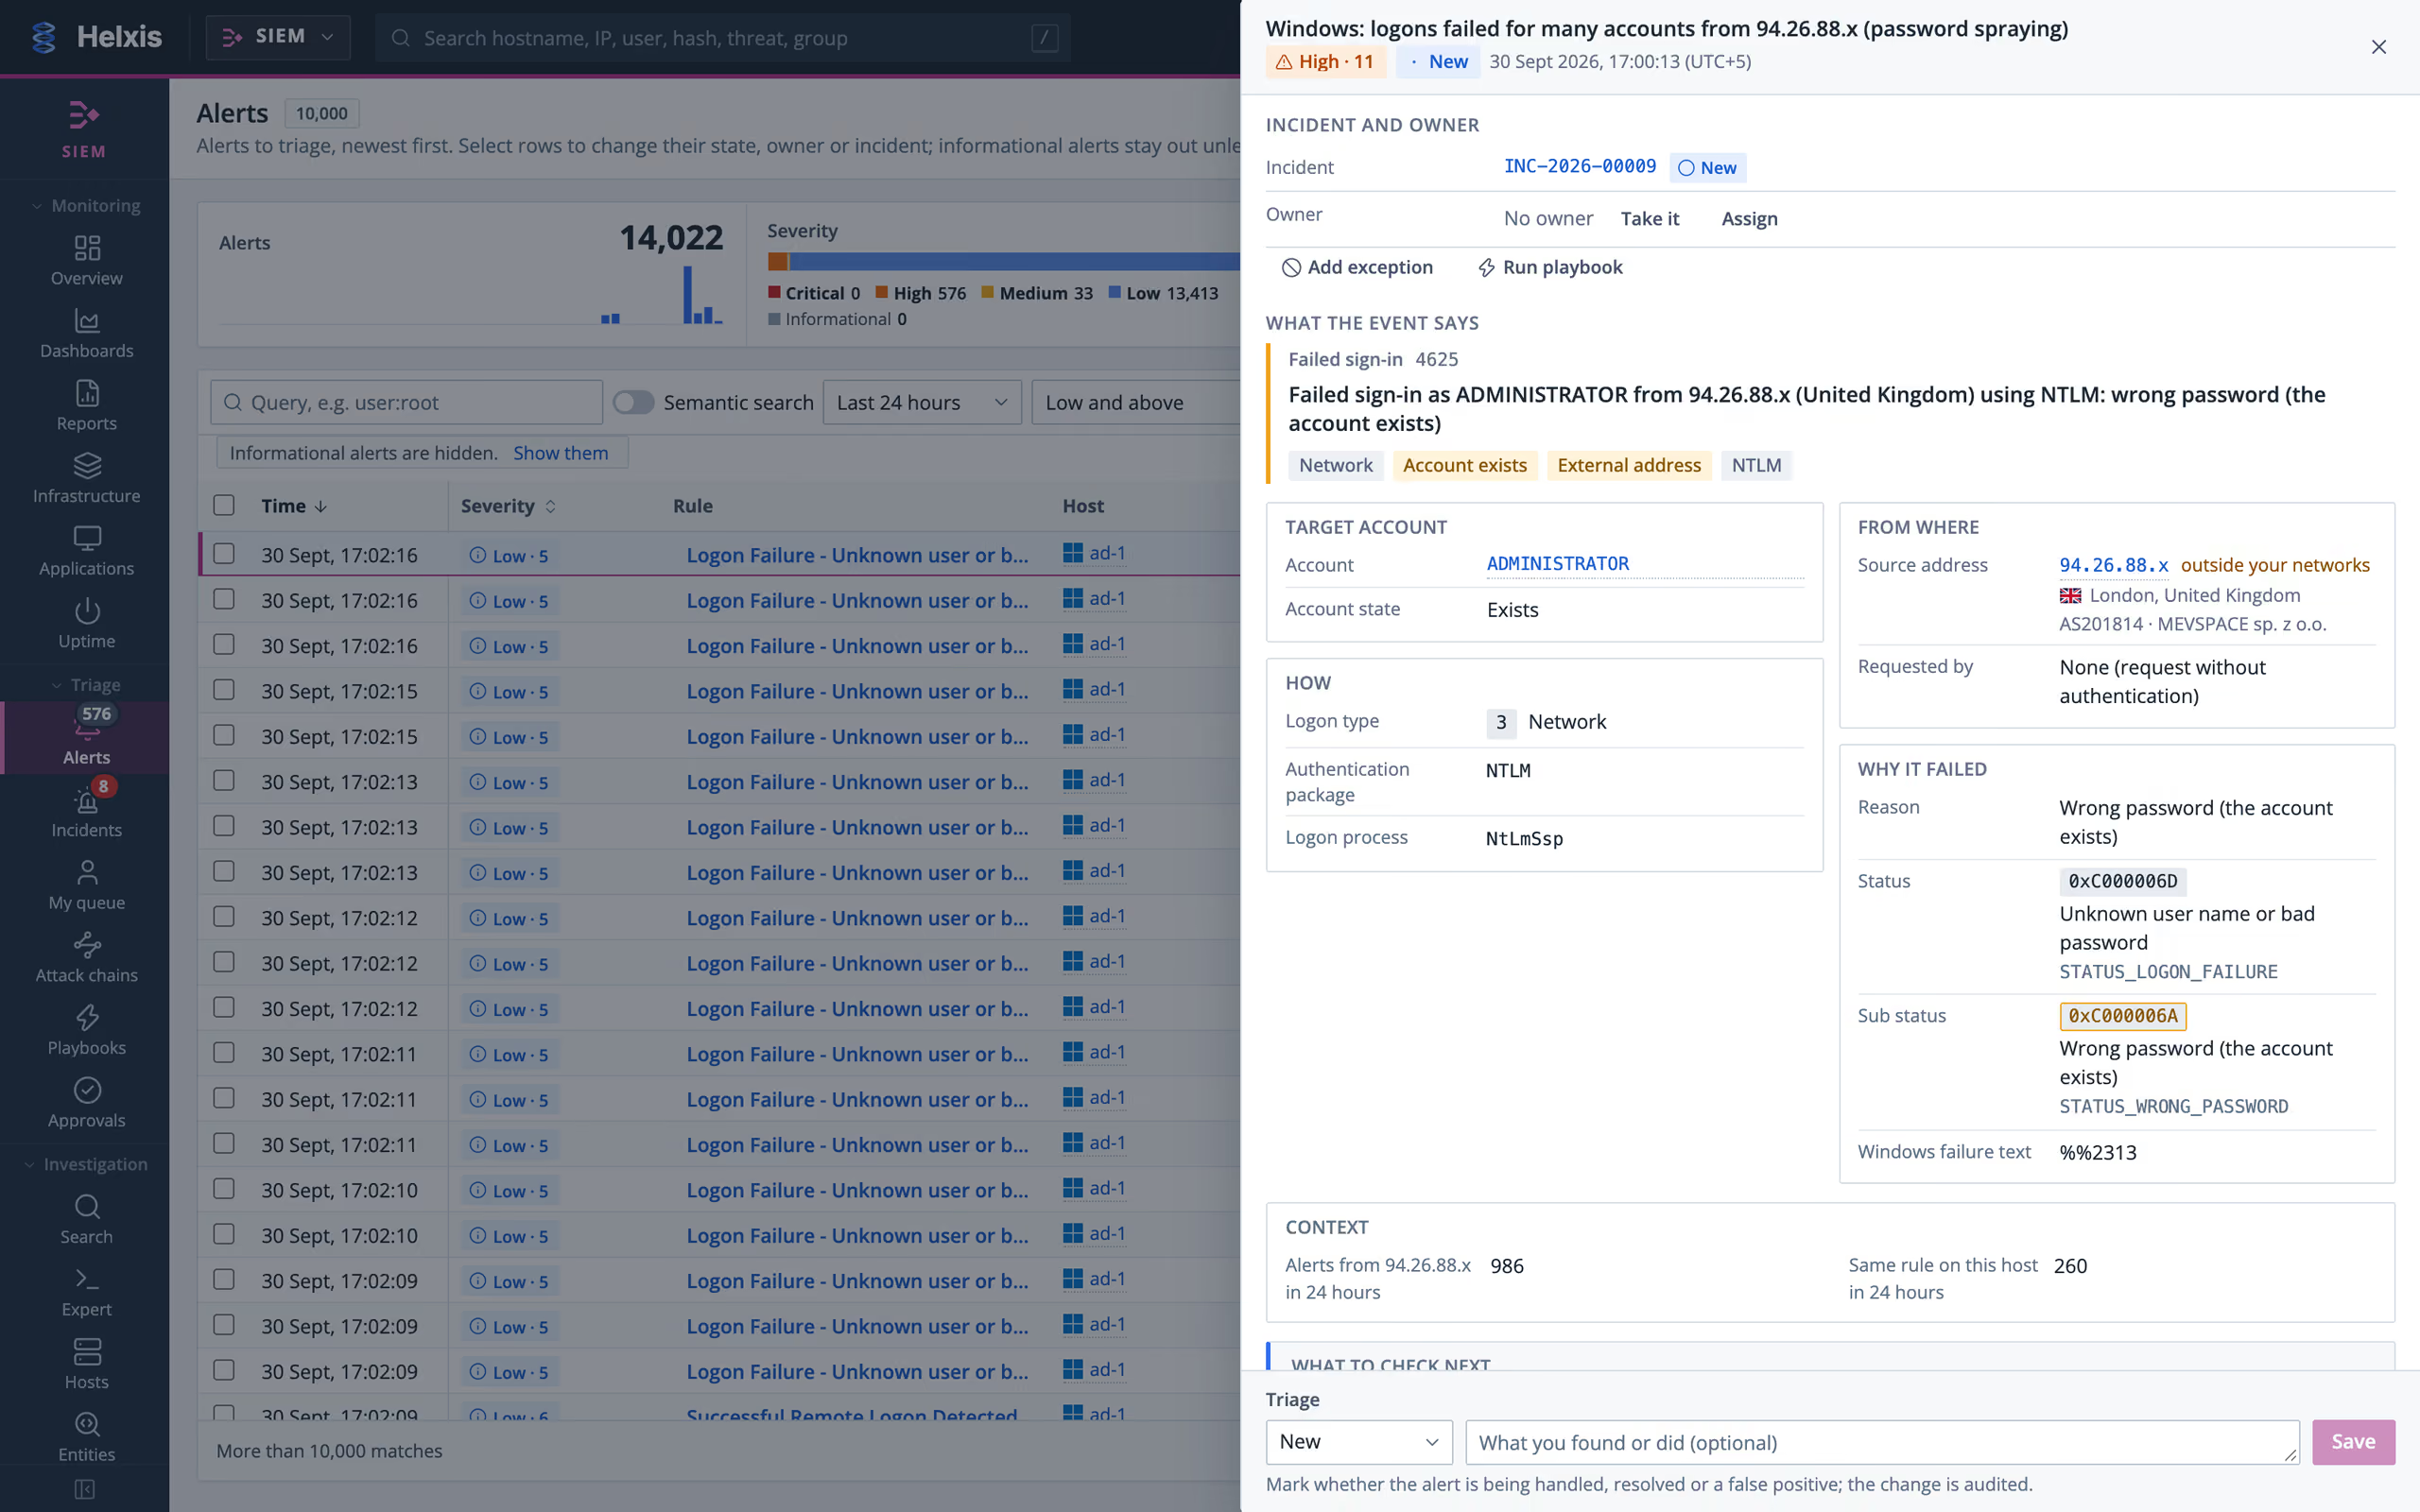
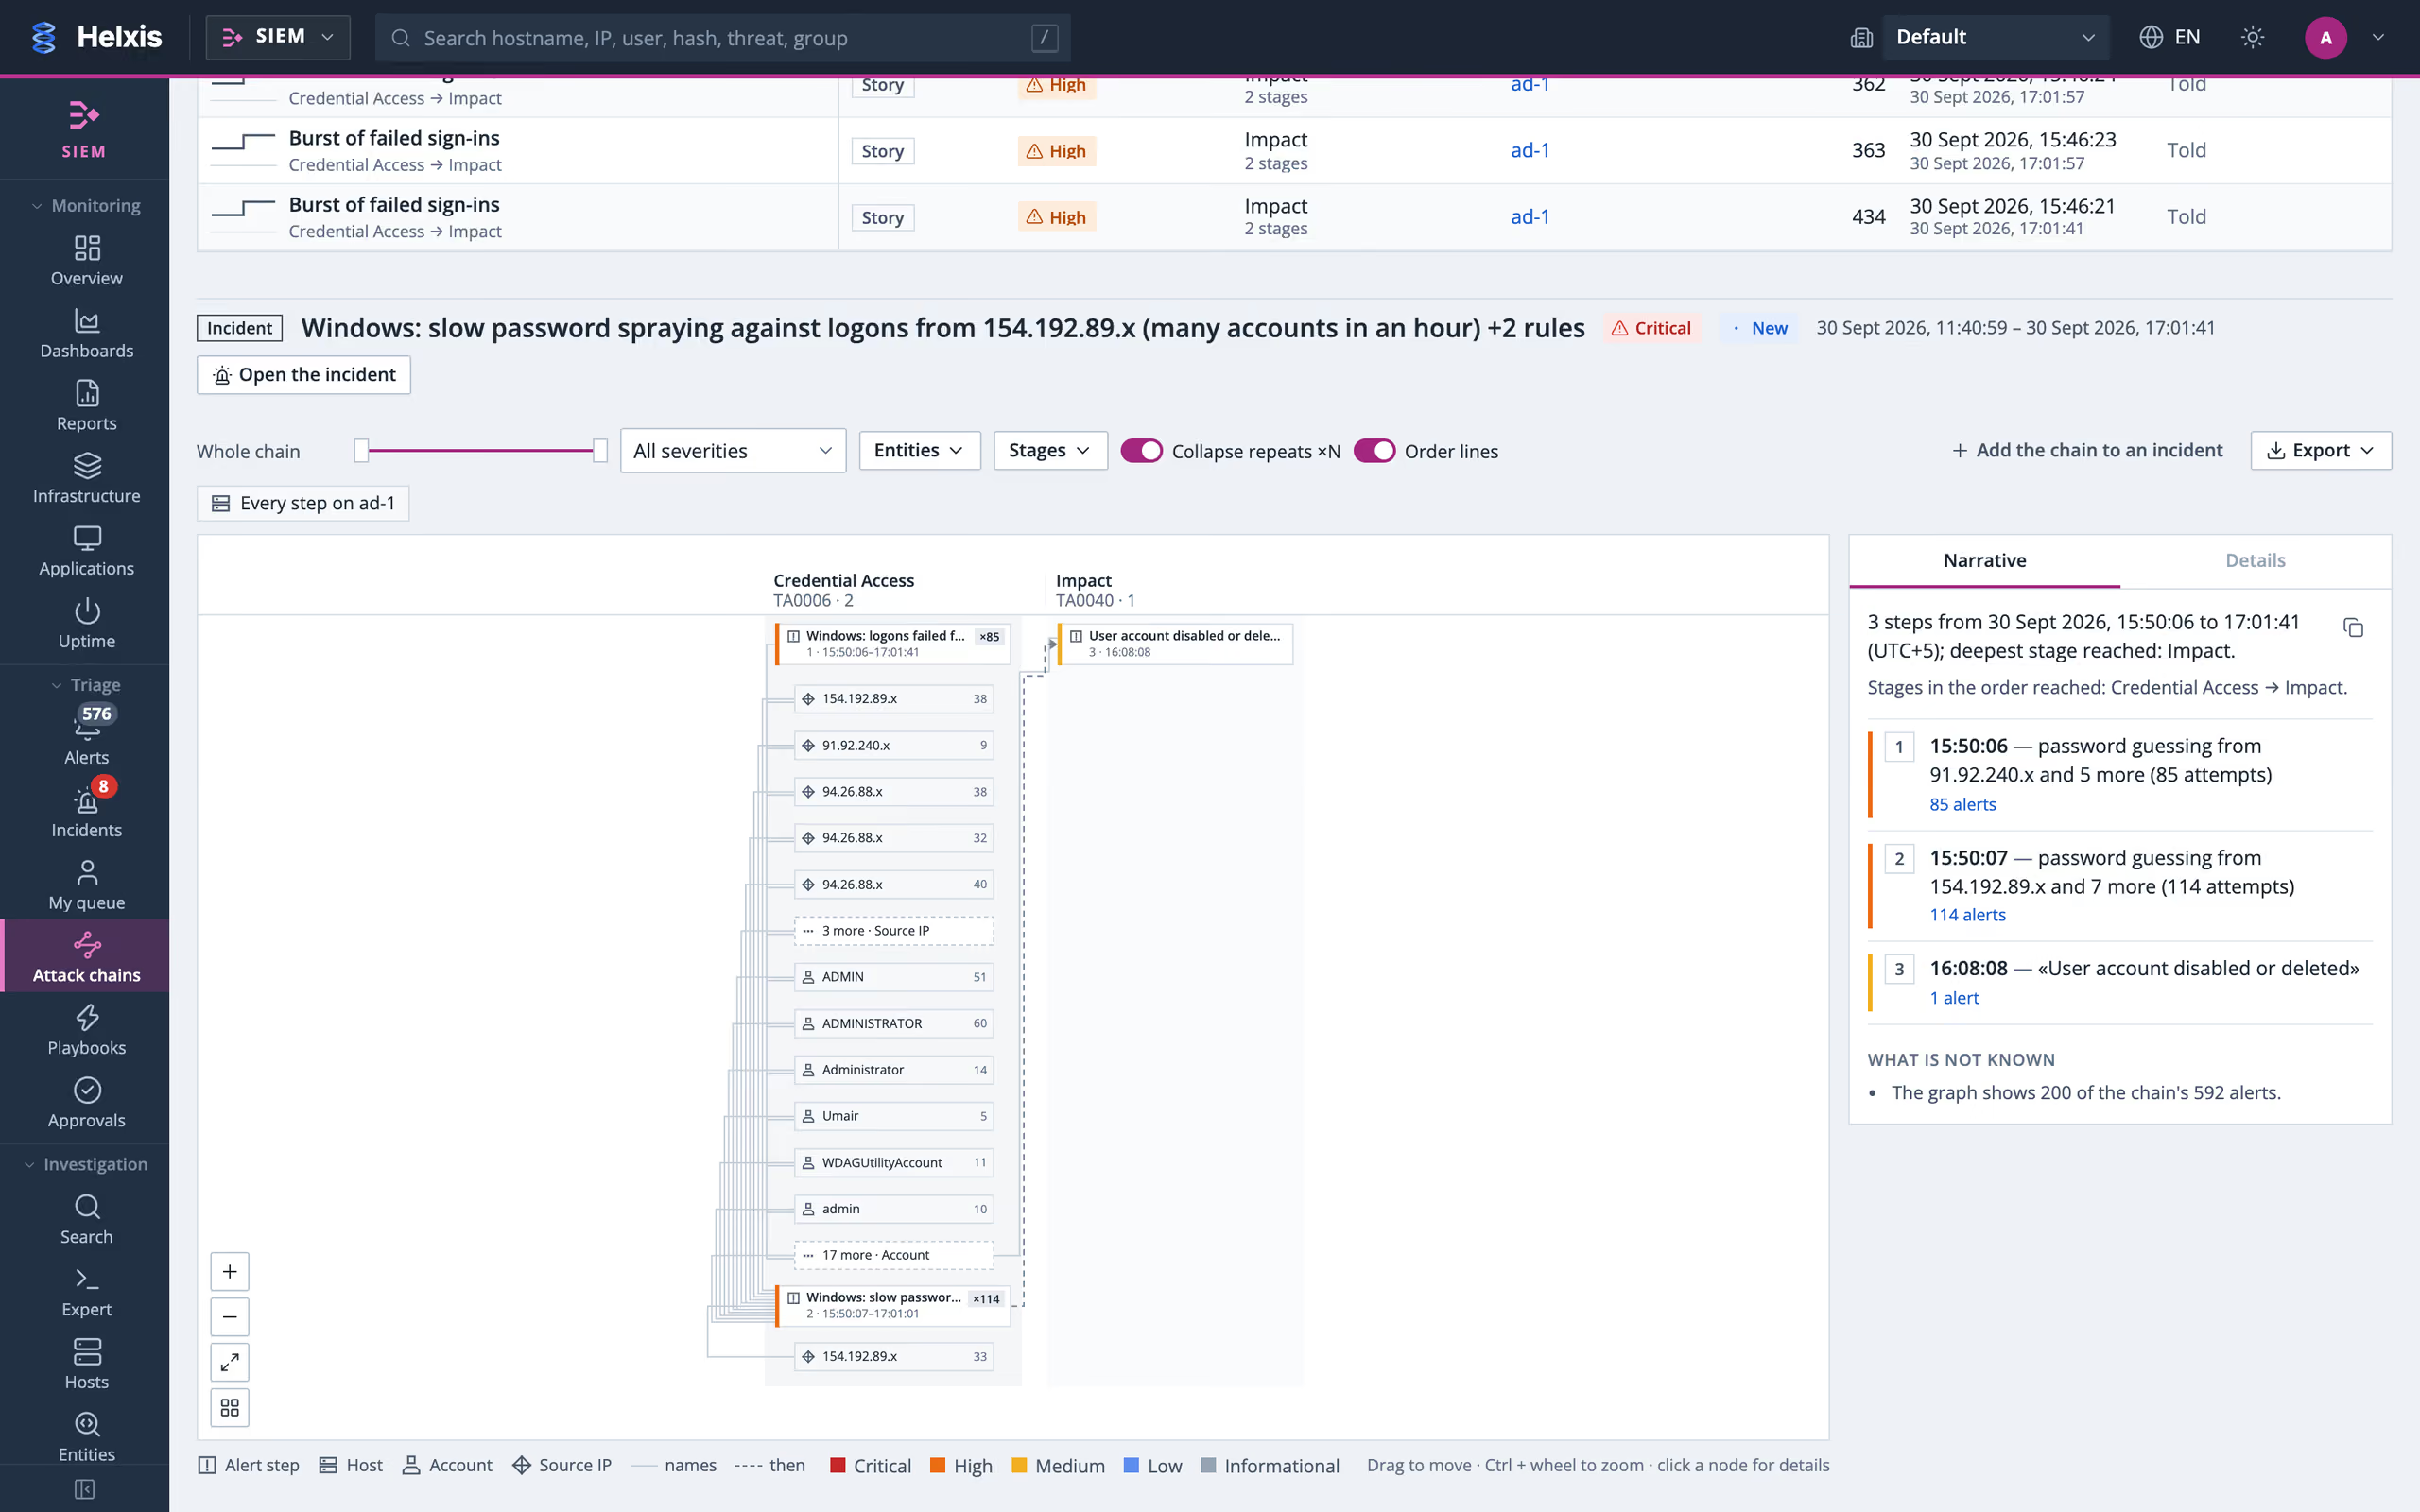
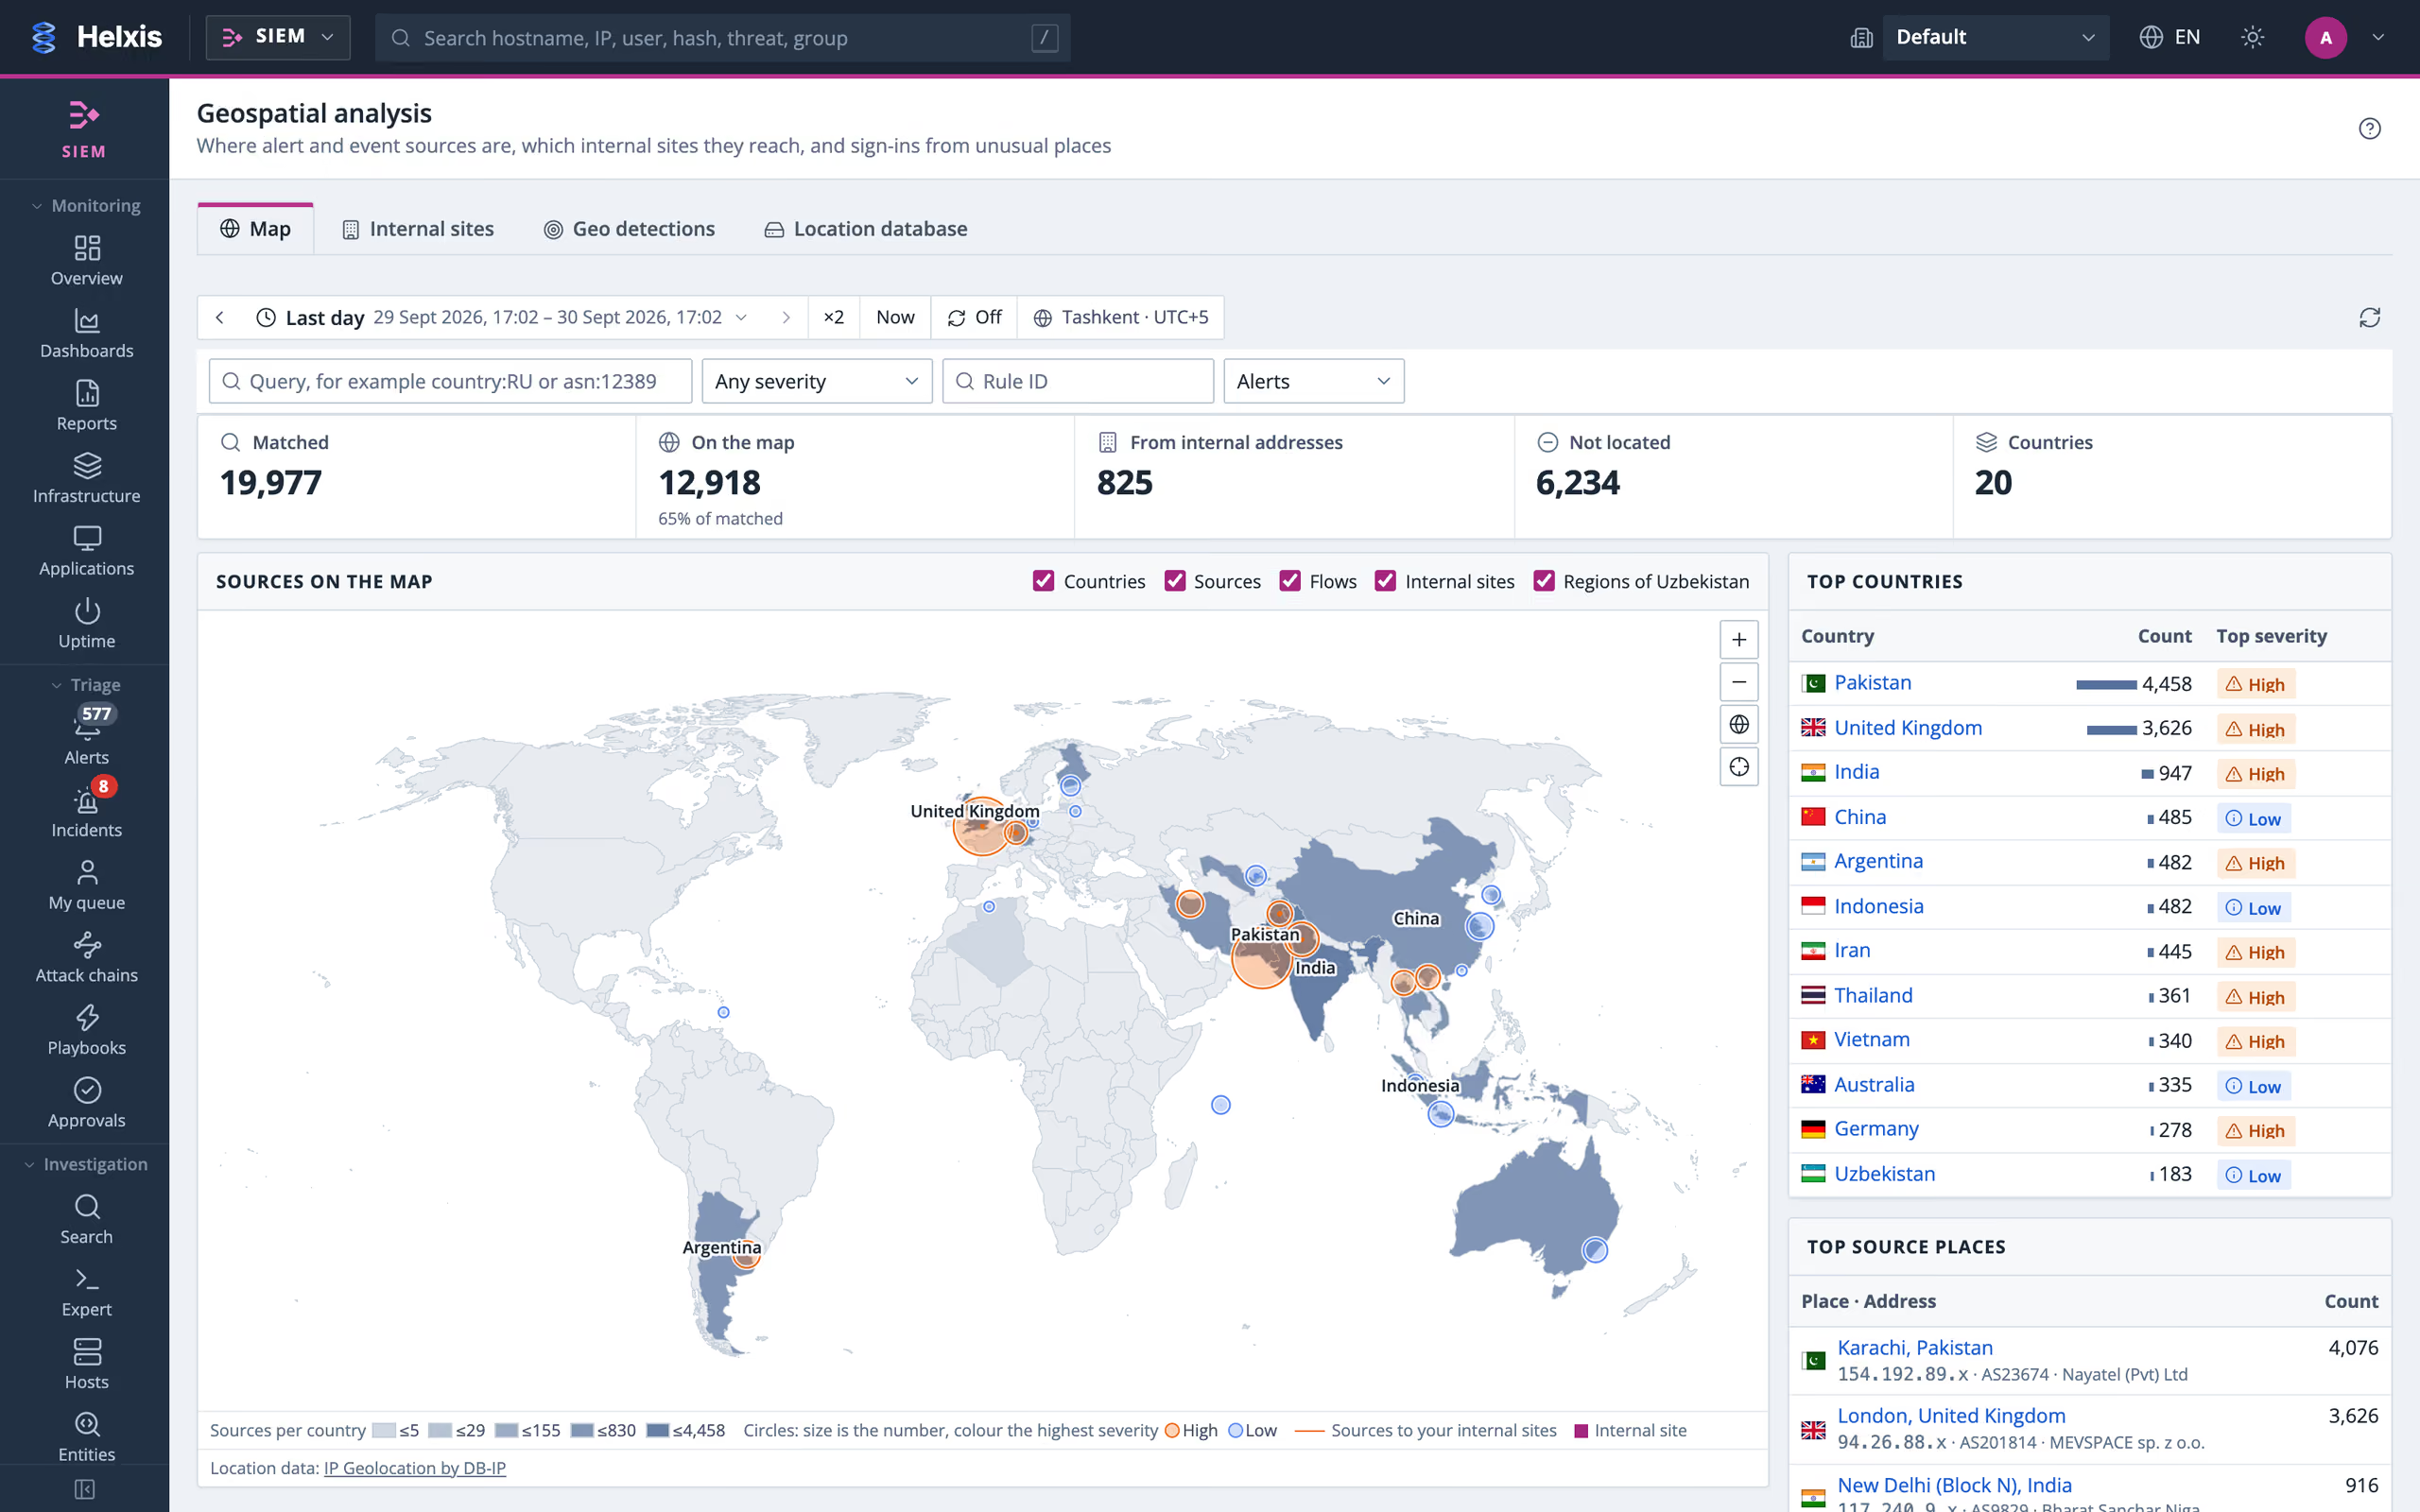
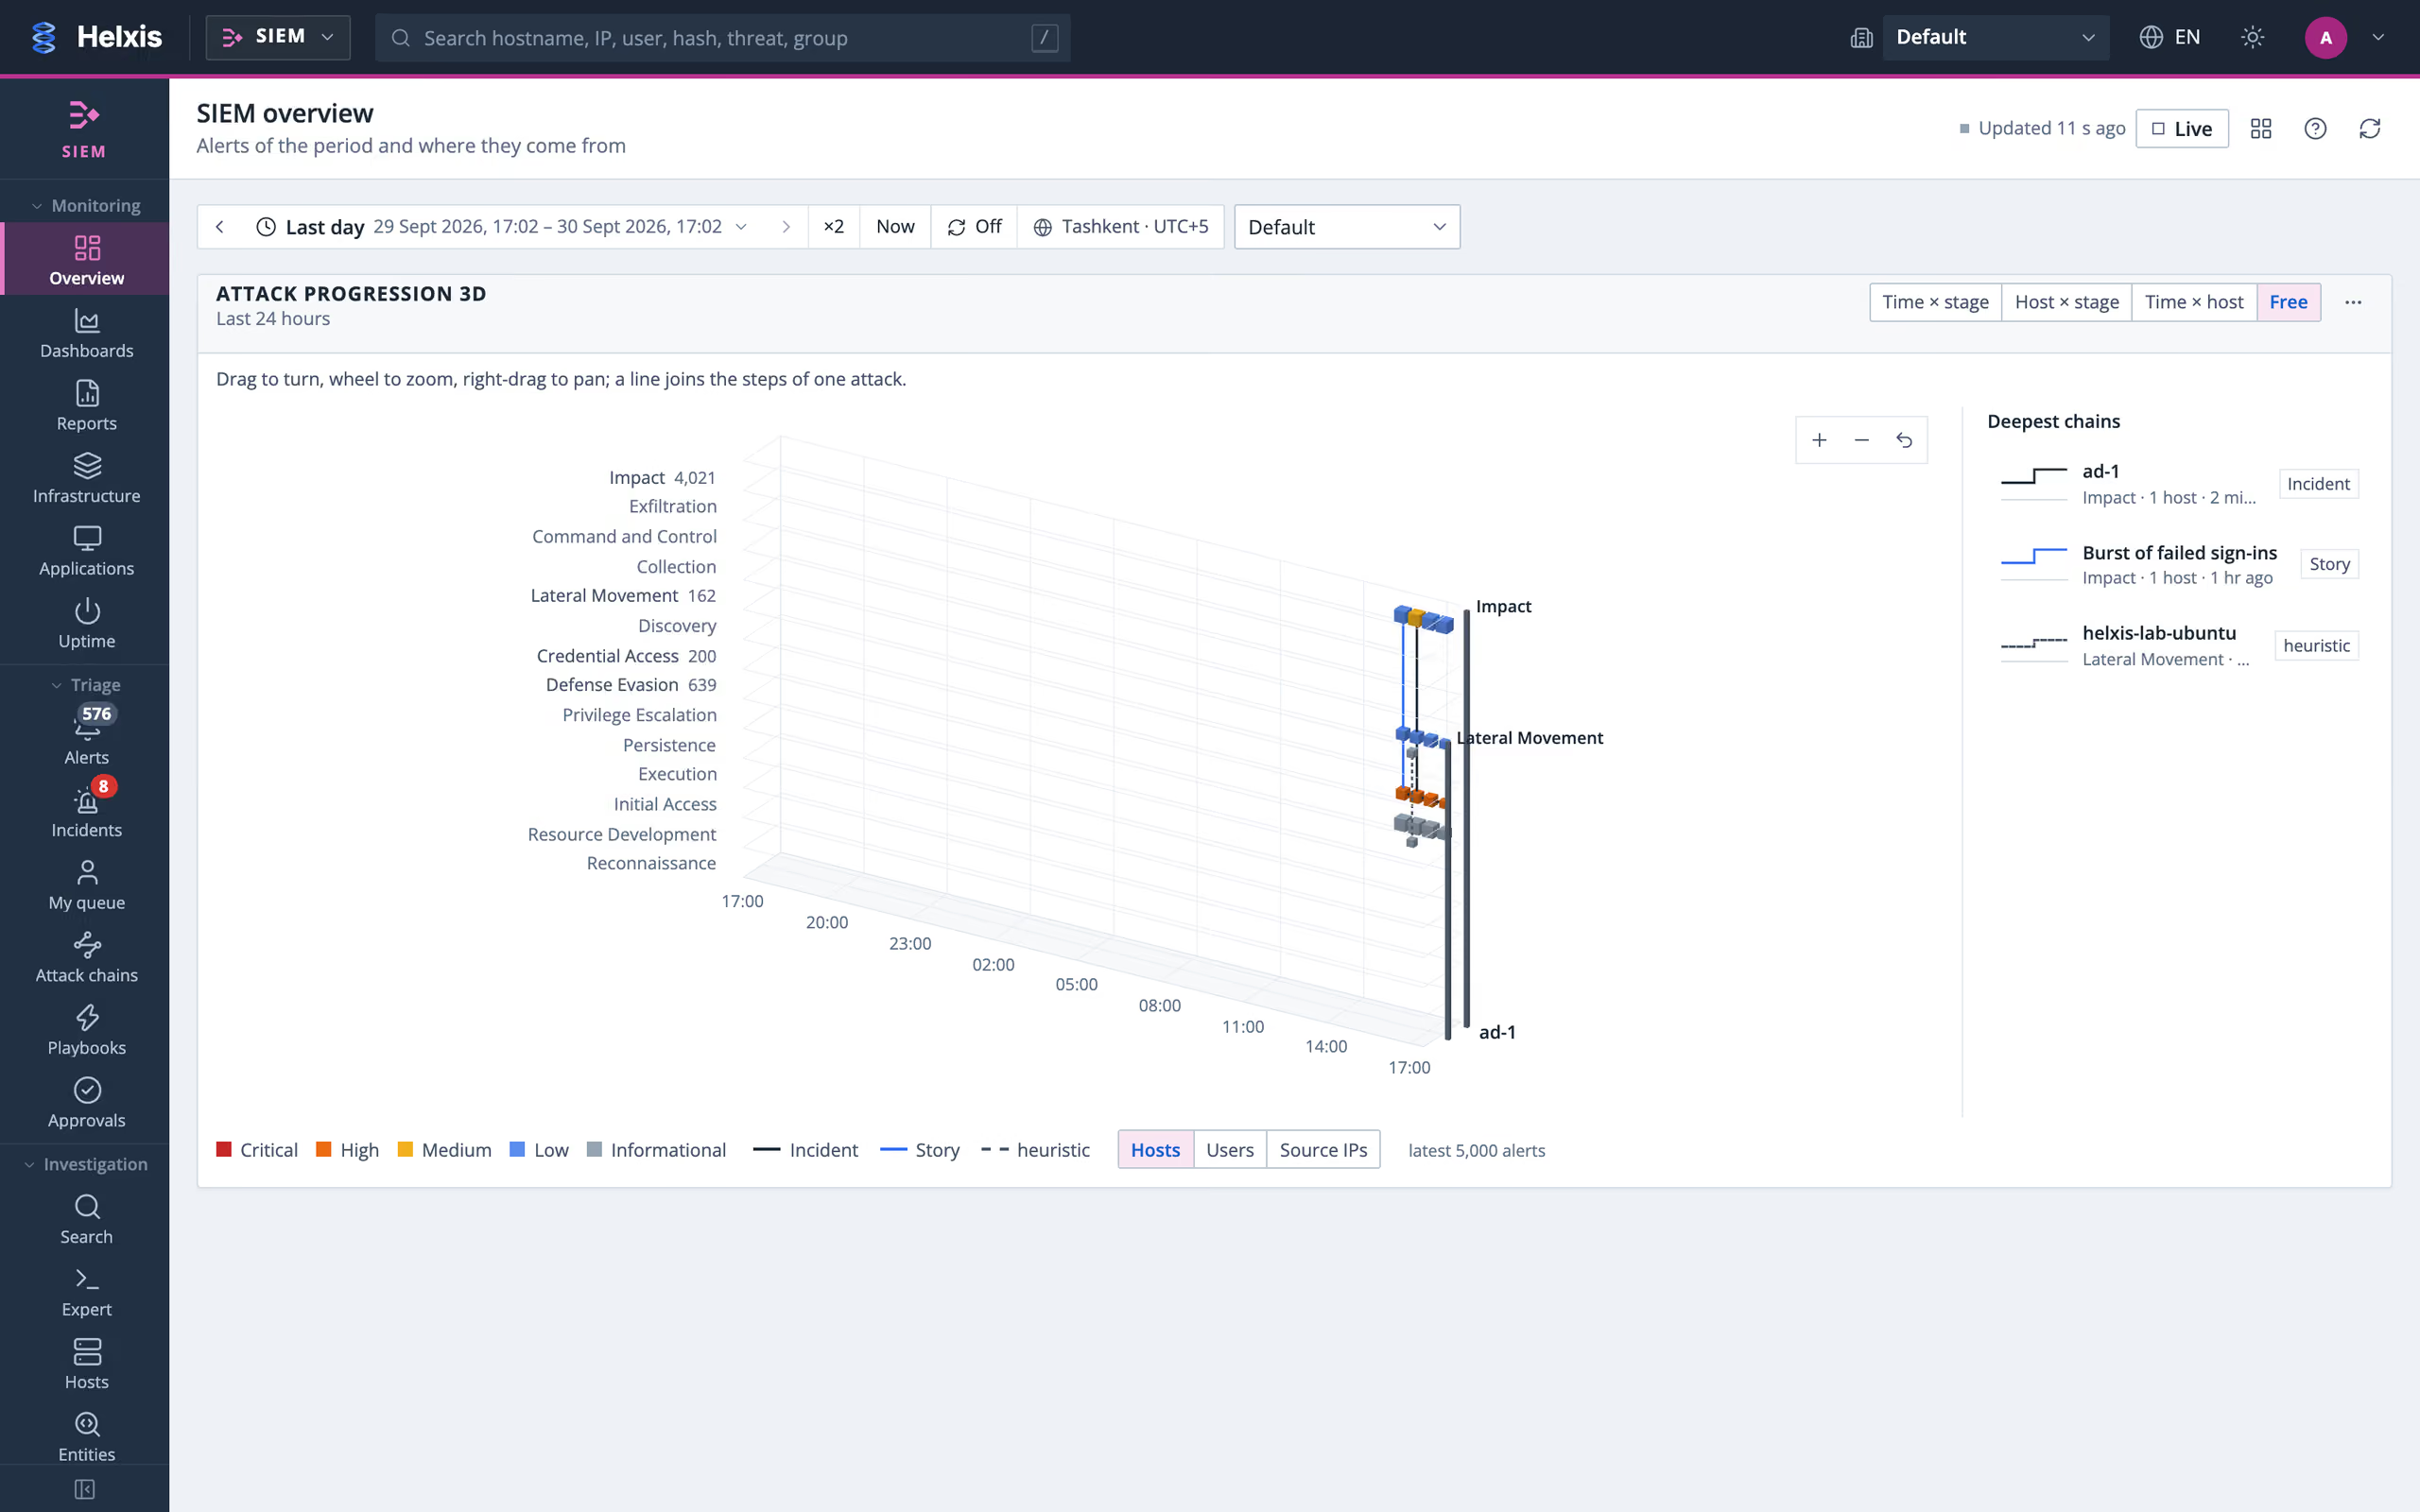
Four console screens: a kill chain analysis, a Windows event explained, an attack chain and a map of alert sources. These are working screens of the product, not mock-ups.

Three-dimensional view of how attacks progress through the MITRE ATT&CK stages over time, with the deepest chains on the right

How attacks progress through the MITRE ATT&CK stages on a three-dimensional scene: time, stage and host (or user, or source address). A line joins the steps of one attack, and the deepest chains are listed on the right.

Open at full size

The screens were captured in a test environment with real data: a Windows Server 2022 domain controller that receives real password-guessing attempts from the internet, and a Linux web server. Source IP addresses are shortened and the addresses of the hosts themselves are replaced.

EPP at work

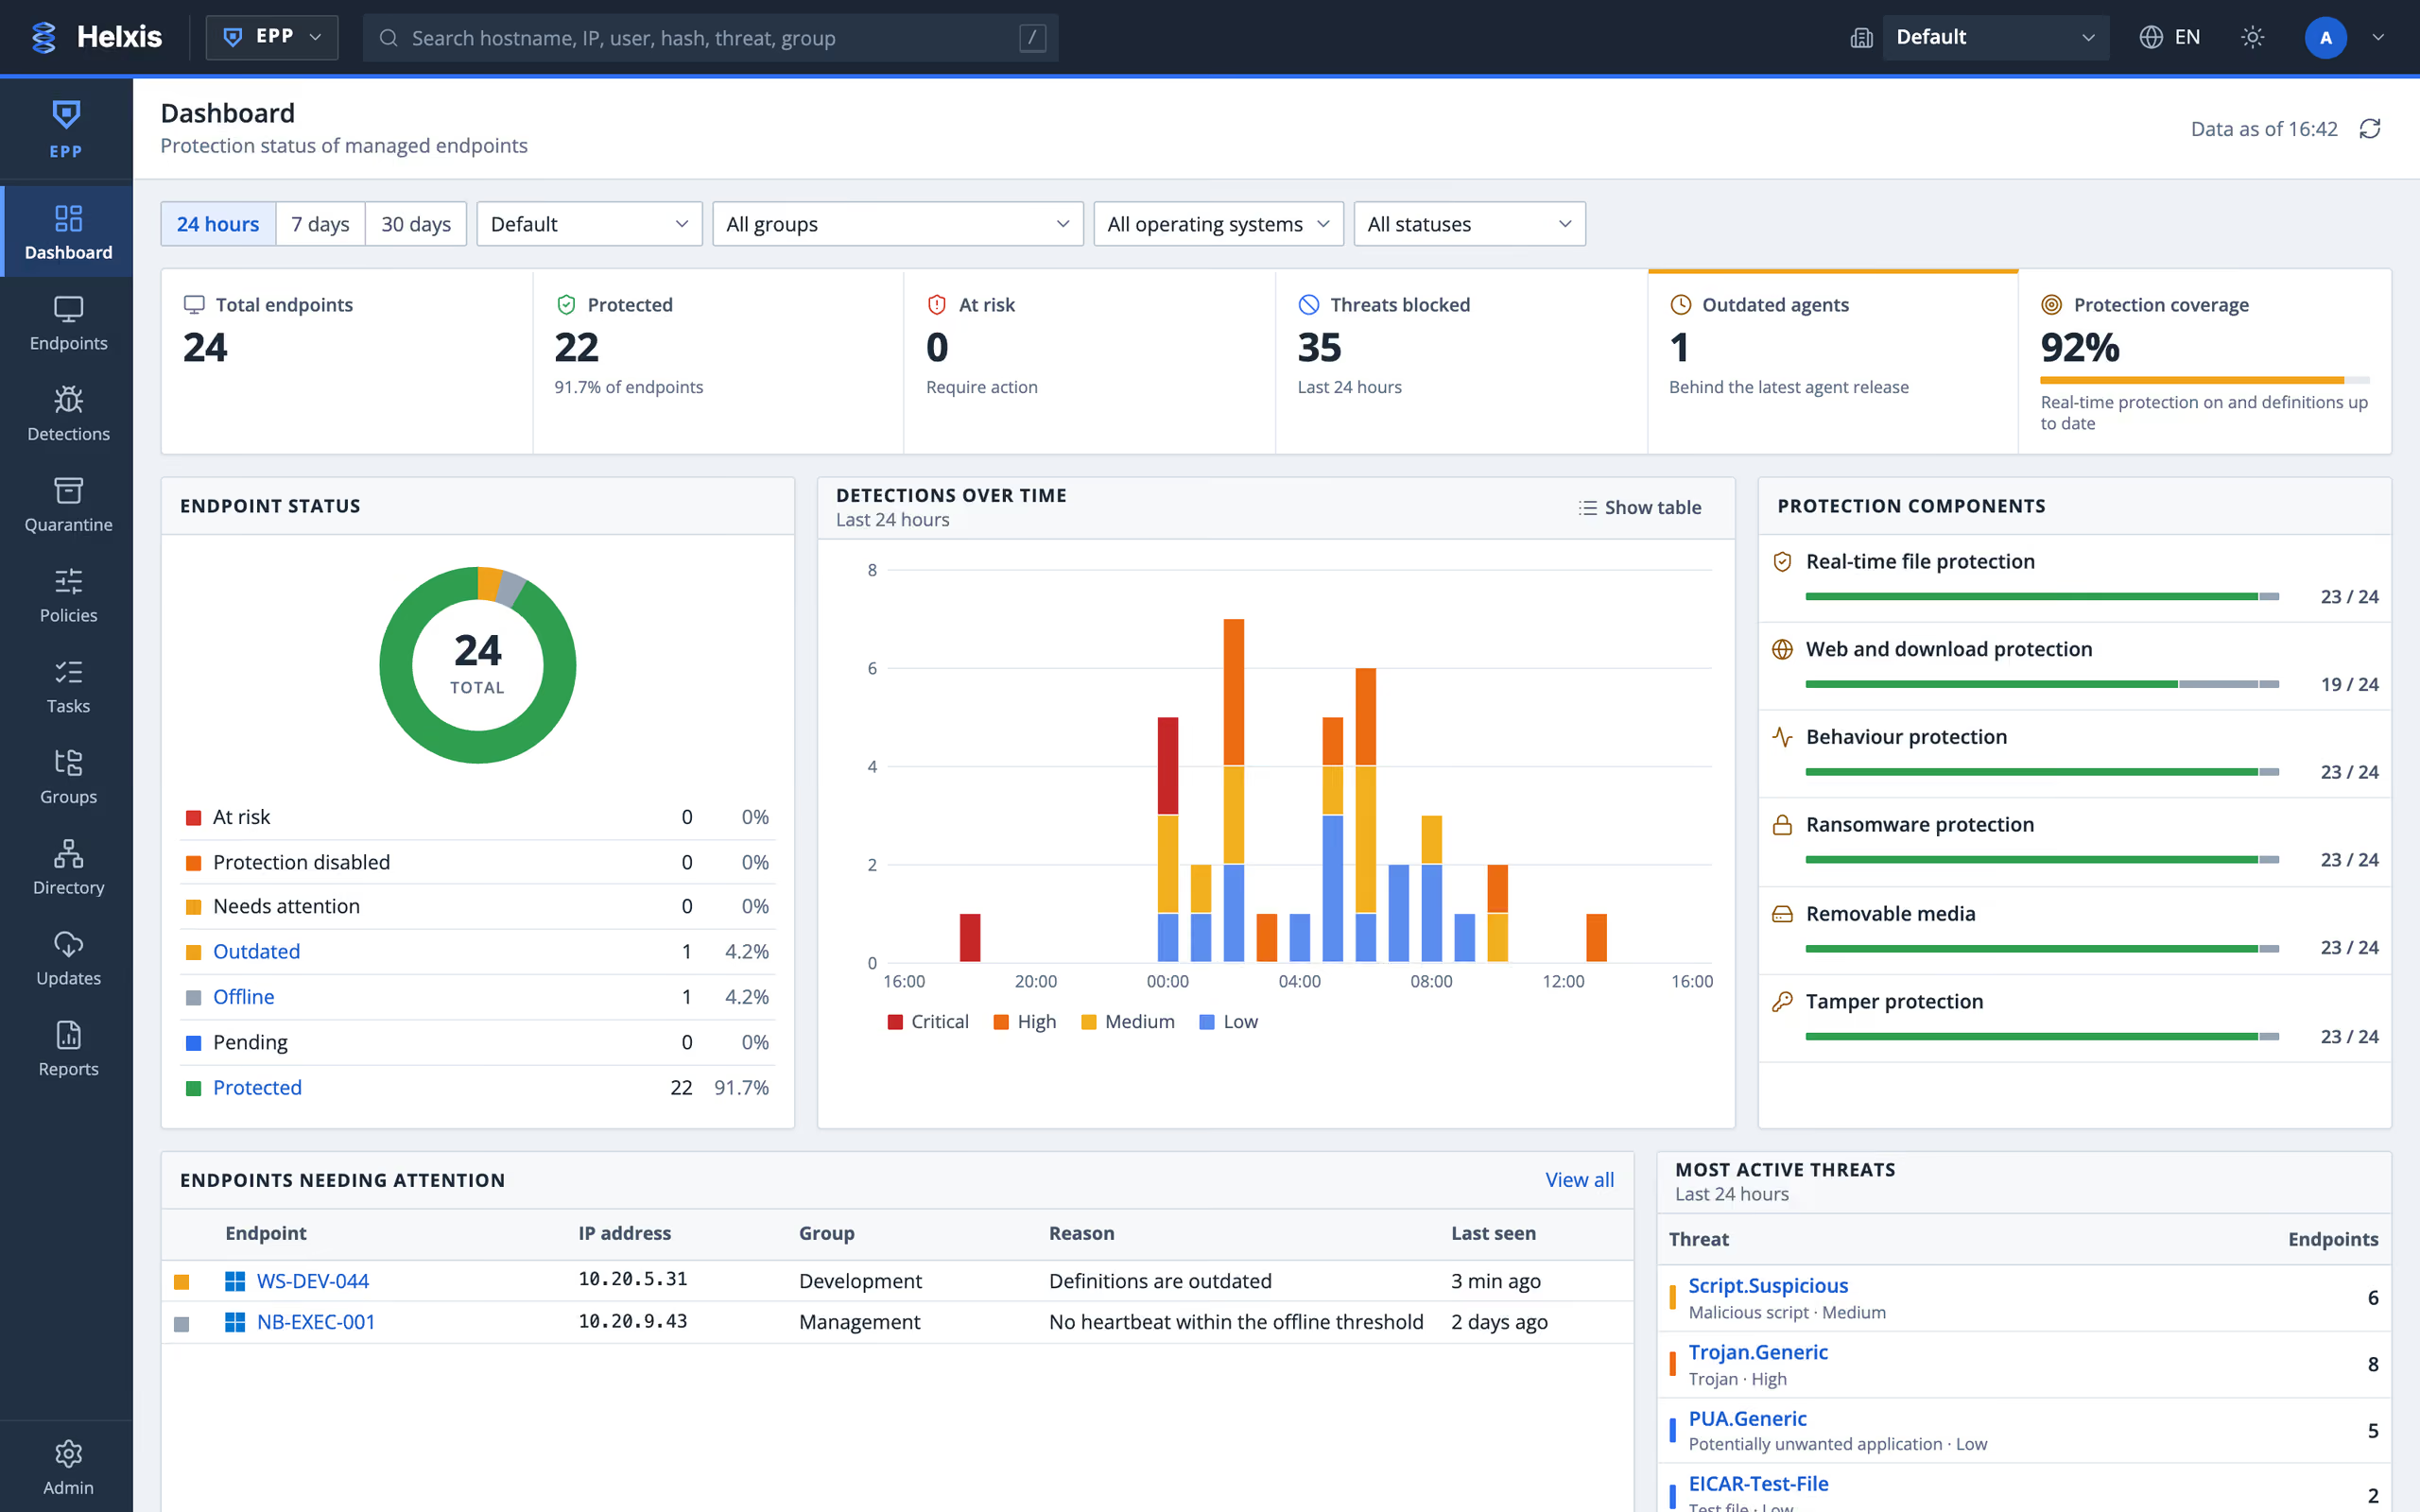
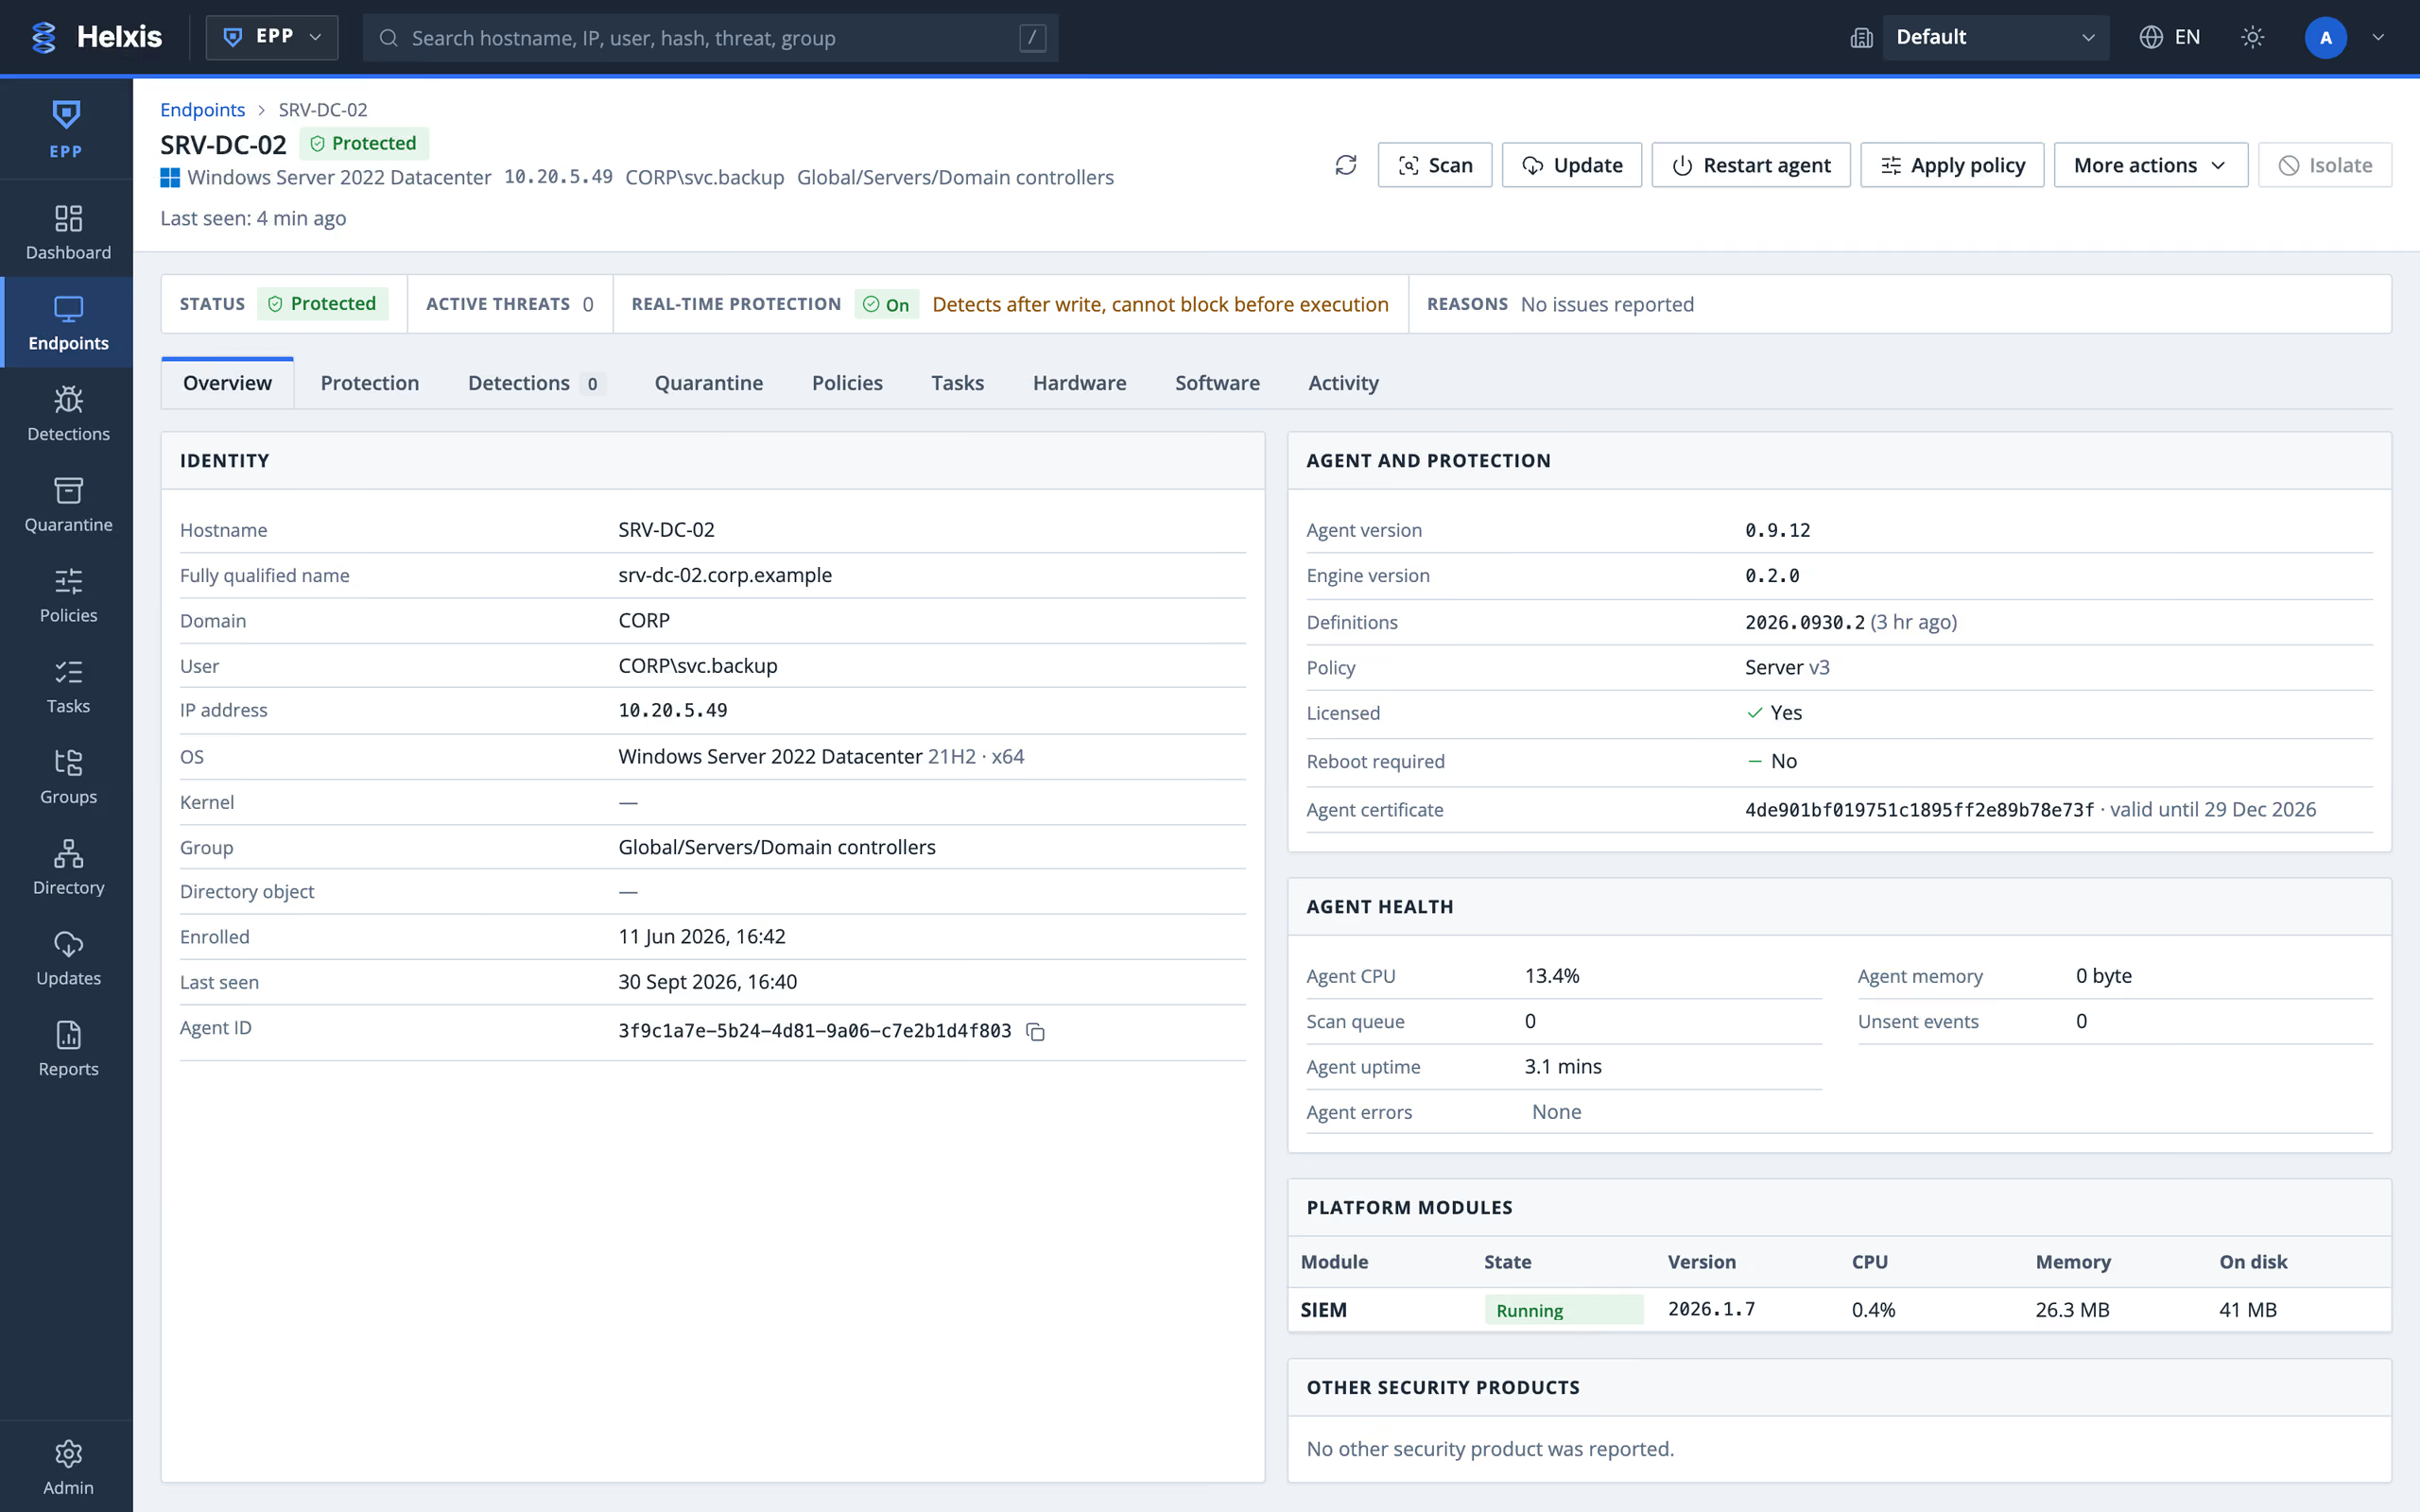
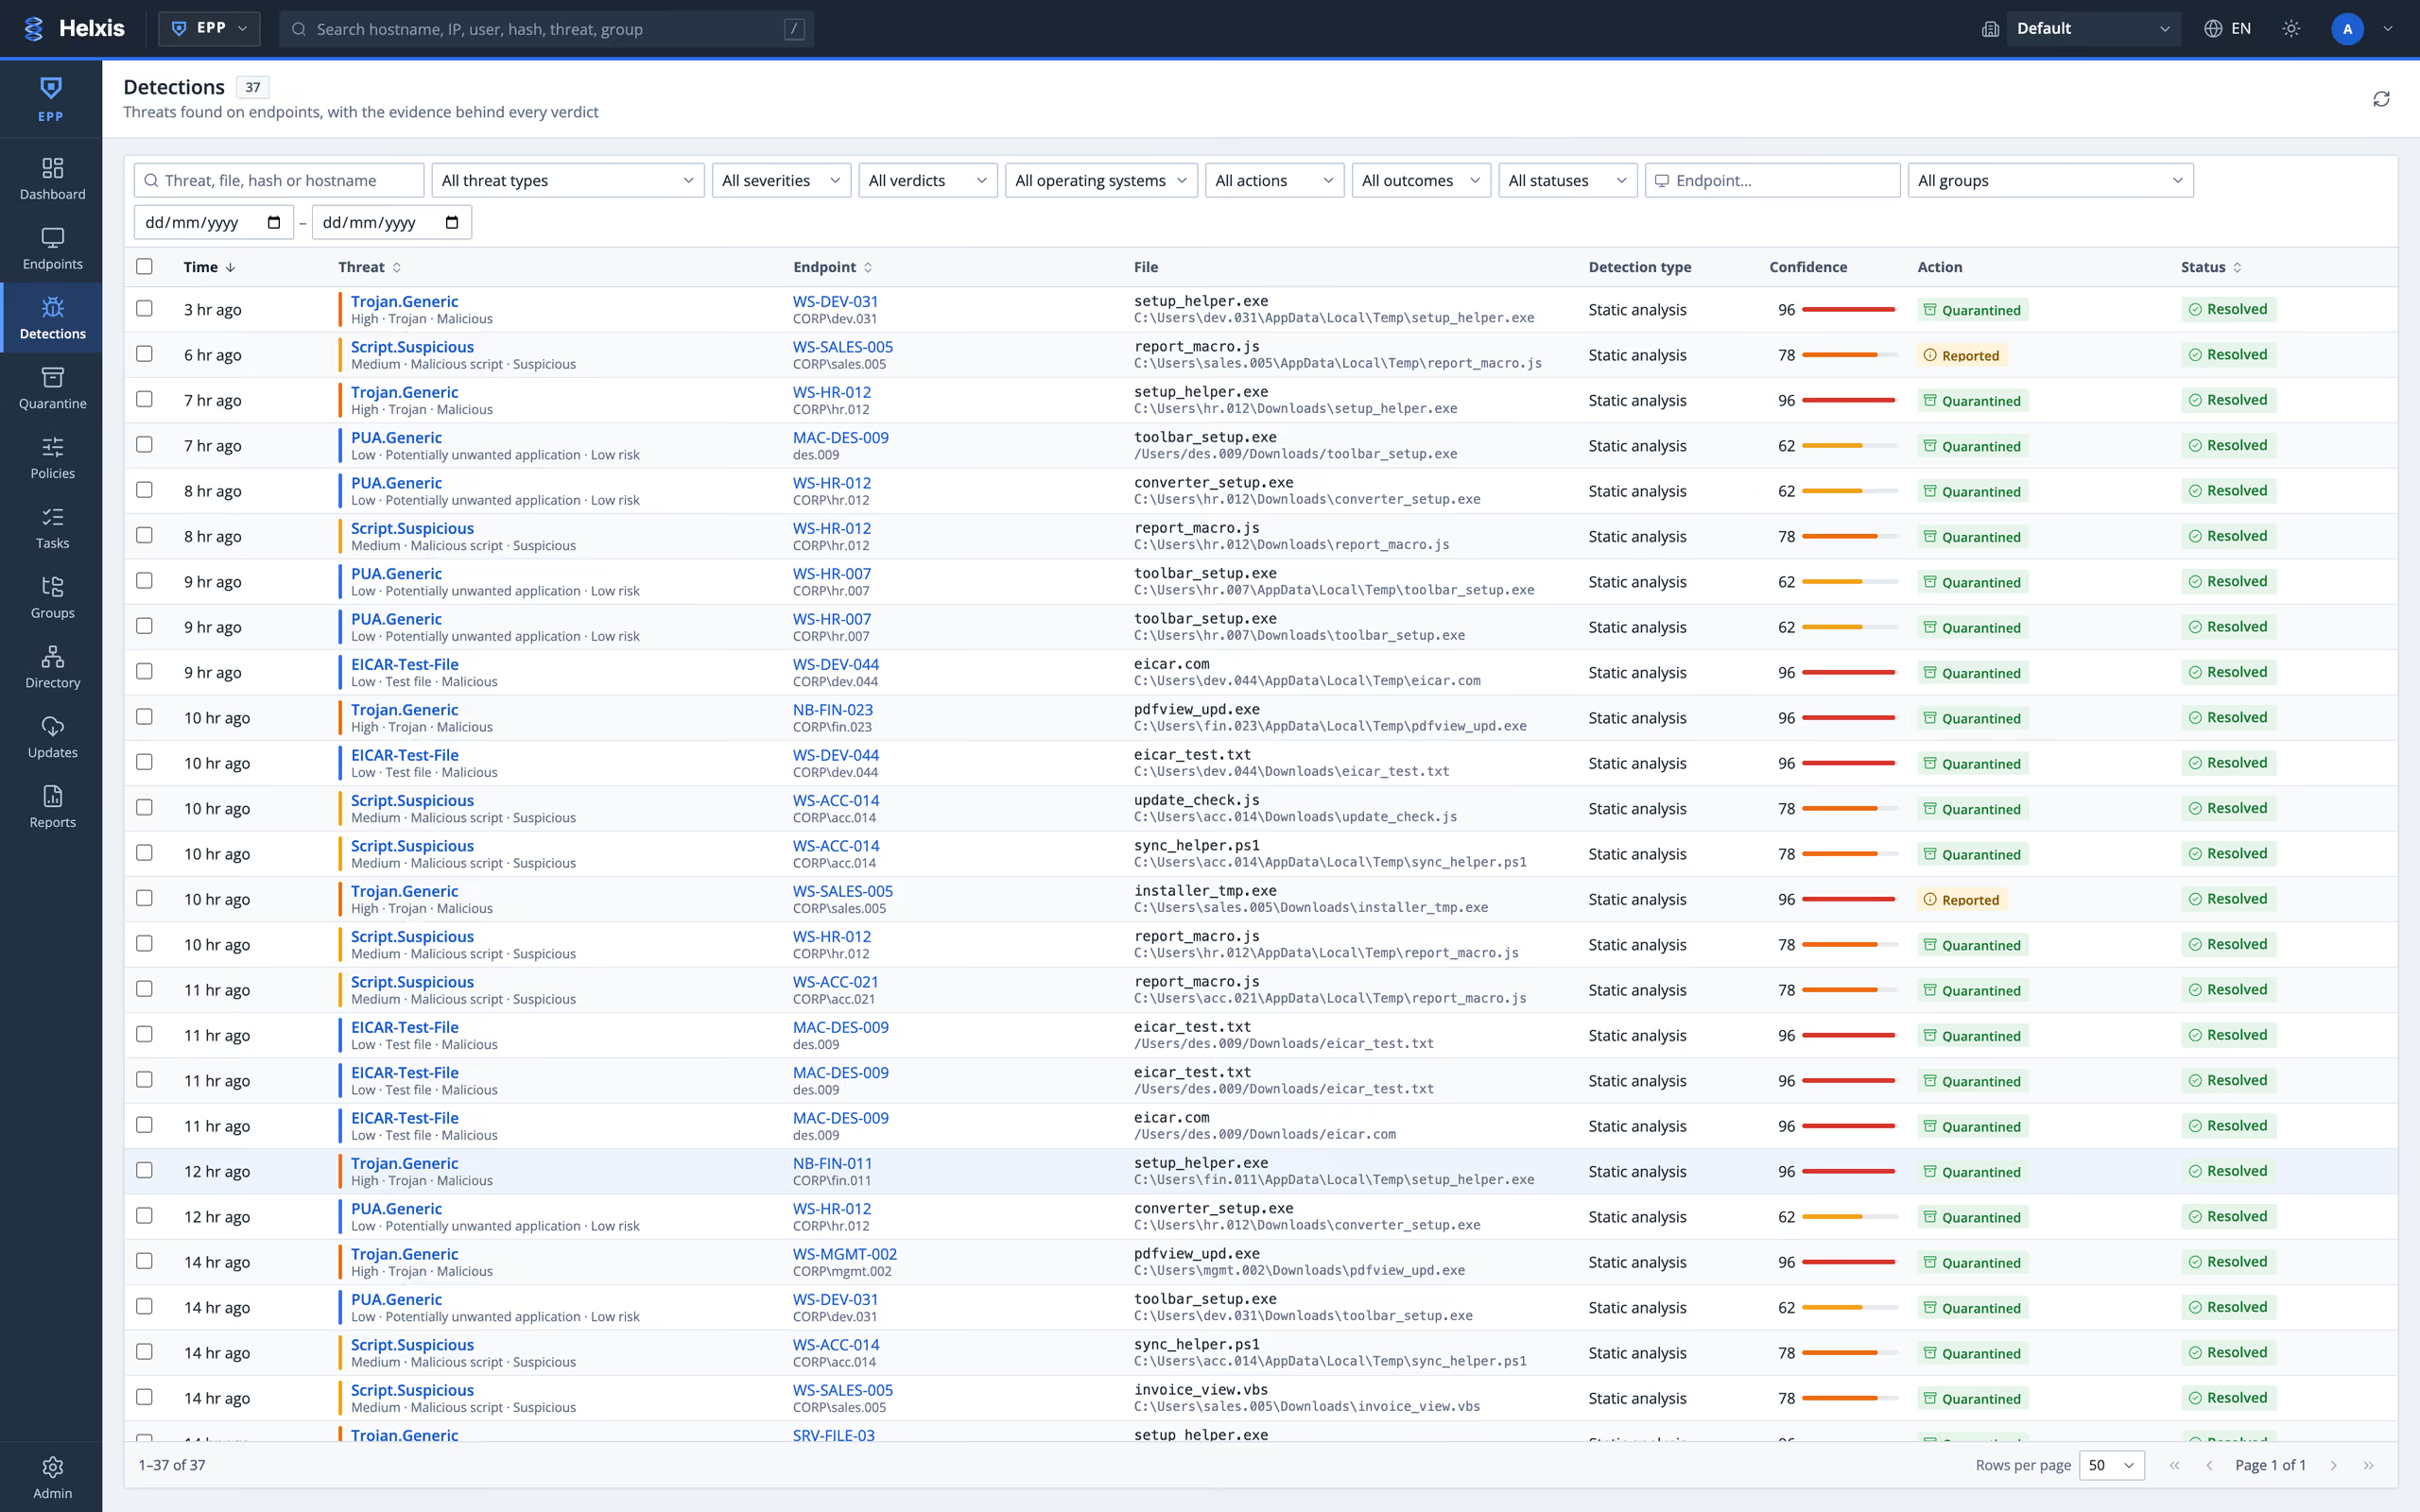
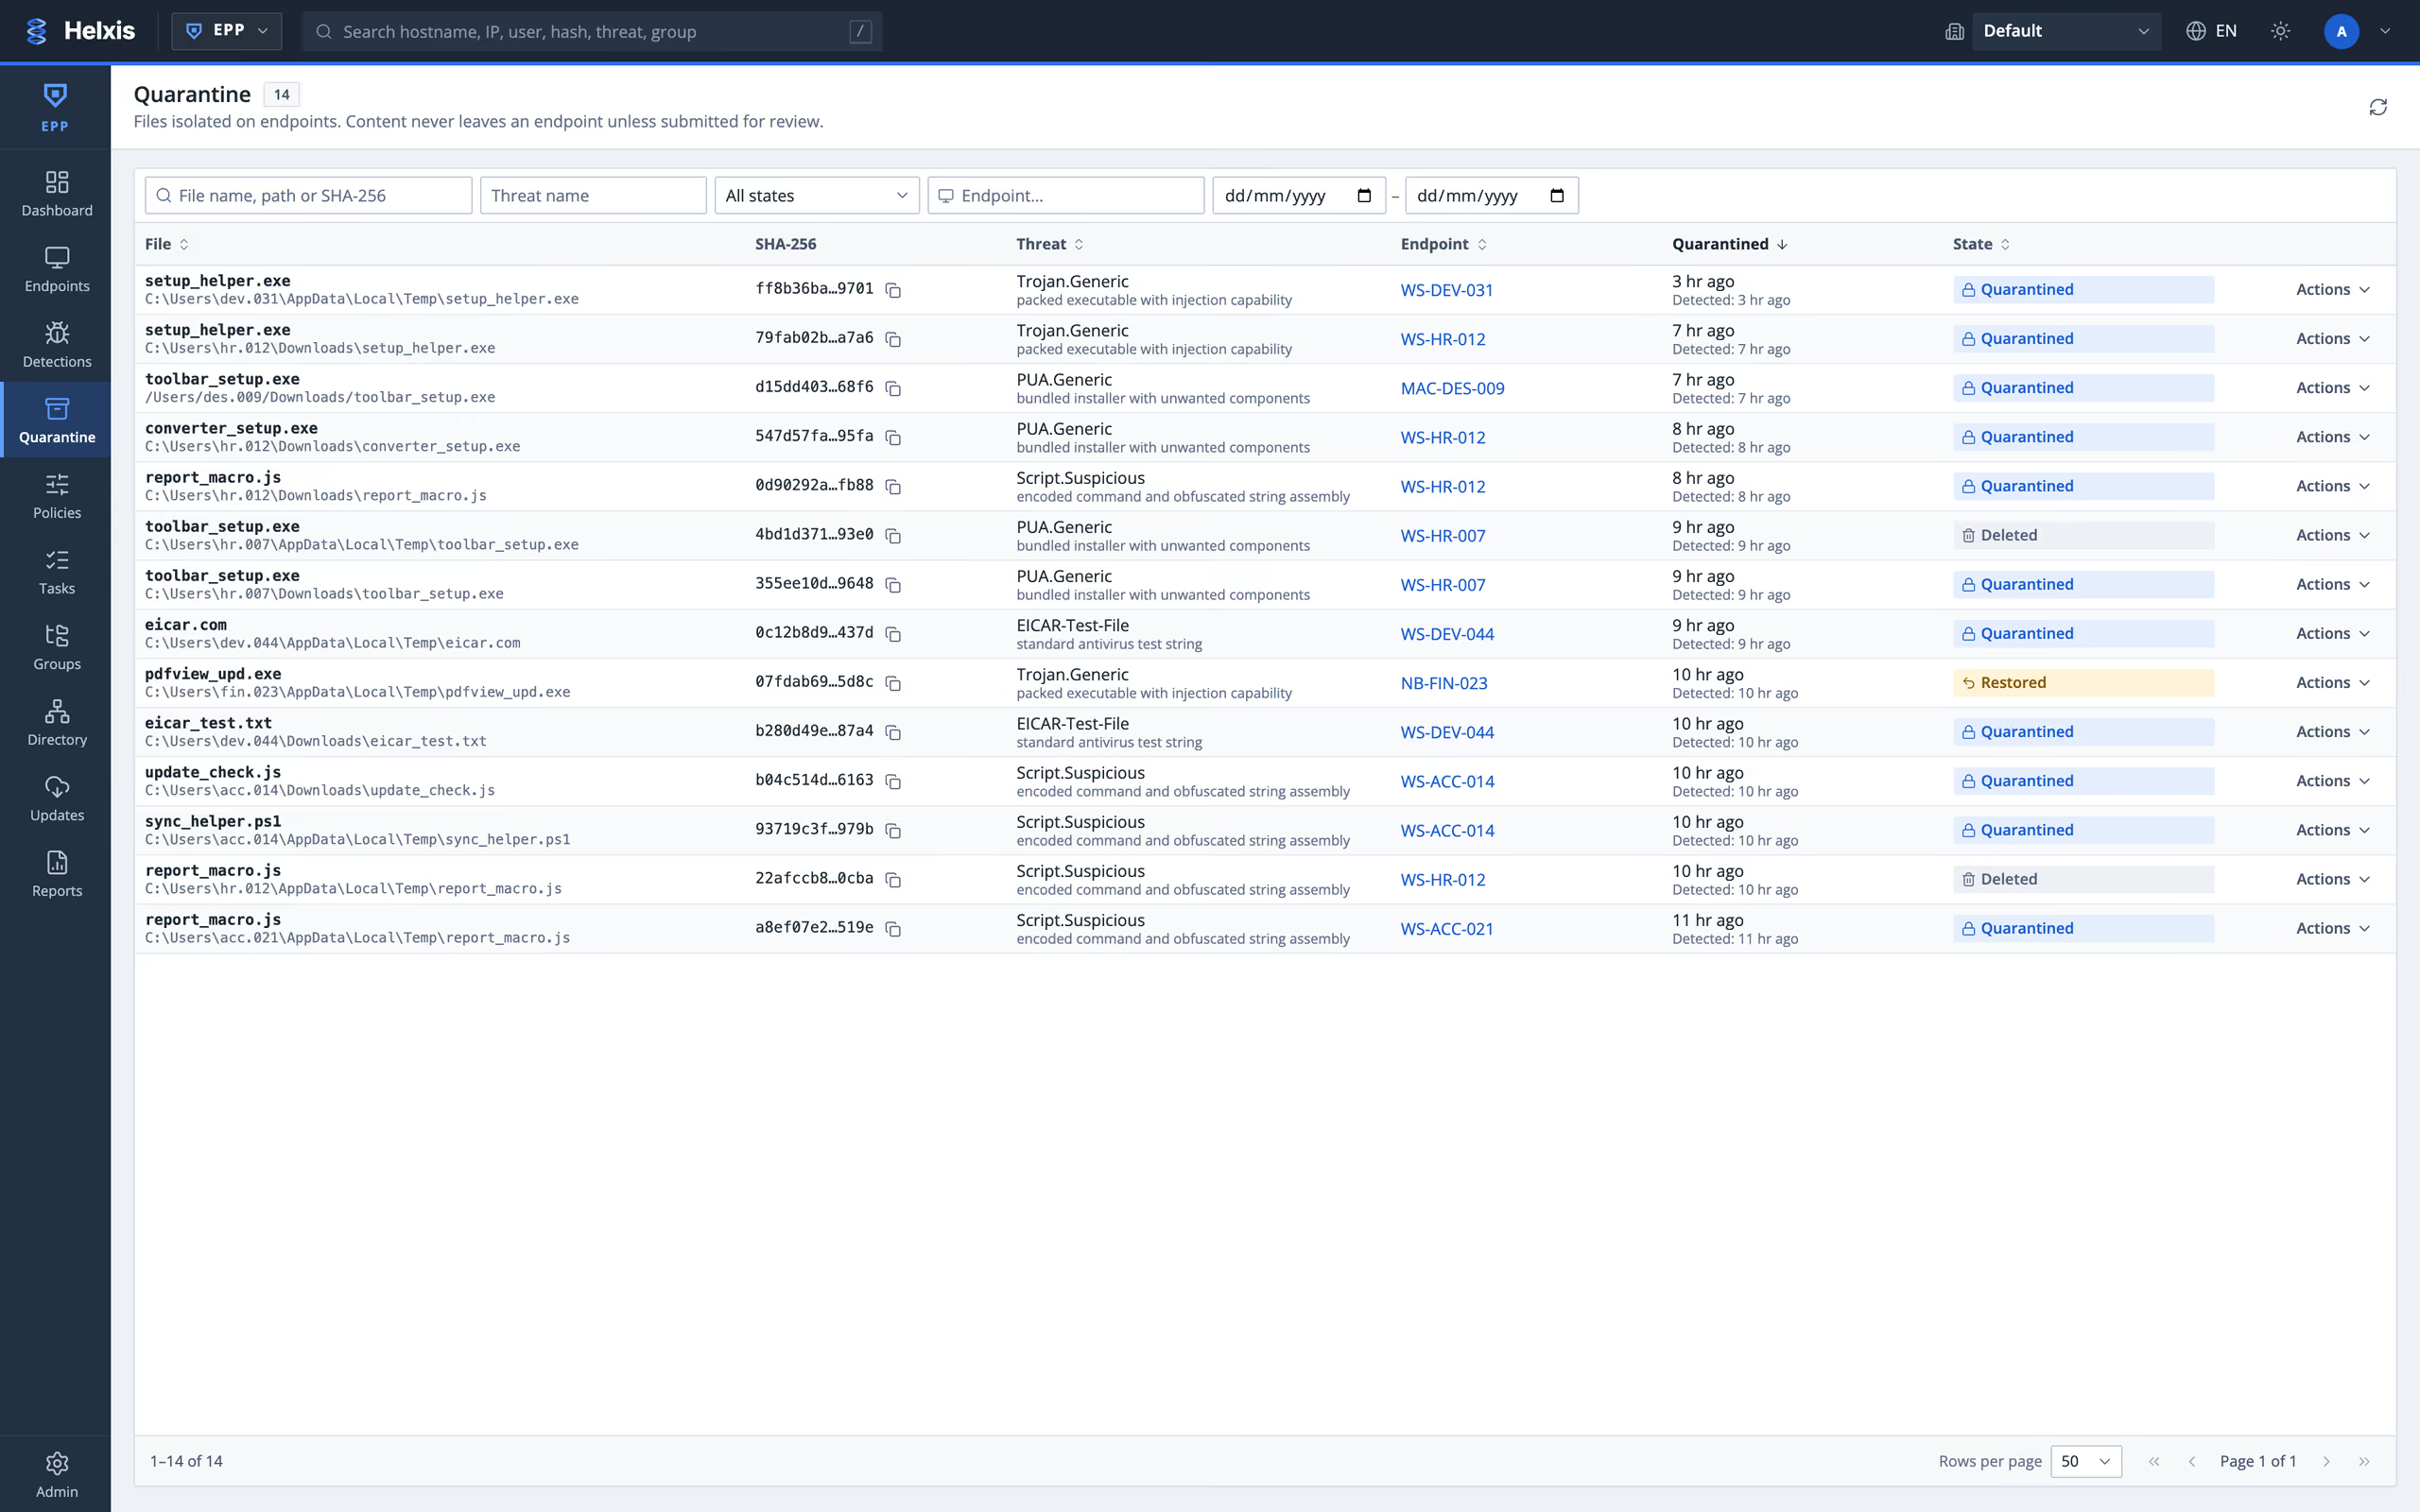
Four screens of the endpoint protection console: the dashboard, an endpoint card, detections and quarantine.

EPP dashboard: endpoint status, detections over the day, protection components and the most active threats

Fleet state on one screen: endpoint status, detections over the day by severity, protection coverage by component, endpoints needing attention and the most active threats.

Open at full size

The screens were captured on demonstration data: a sample fleet of 24 endpoints prepared for the purpose. The interface is the product’s real console.

Storage: Three Tiers And Retention Profiles

An event moves between tiers by age, by tier volume or by space used. Retention is set per source class; events that entered an incident follow their own policy.

Typical retention profiles
ProfileHotWarmCold-archive
Short · 30 days7 days23 days—
Base · 90 days14 days76 daysper policy
Extended · 180 days30 days150 daysup to 365 days
Annual · 365 days30 days180 days185 days
Long · 1825 days30 days180 days1615 days

The profiles are example configurations. Typical compression on text logs is 6–12×.

Where It Runs

Functionality is identical across all four options — only image delivery and the scaling mechanism differ.

Deployment options
OptionDeliveryScaling
PhysicalRPM / DEB packages, ISO imageAdding nodes and disk shelves
VirtualisationOVA / QCOW2 / VHDX imagesChanging VM resources, cloning
Private and public cloudVM images, IaC templatesScaling groups, object storage
Containers and hybridOCI images, Helm chartsChanging replica counts, StatefulSet

For multi-site infrastructure a central-node / remote-site scheme applies: a Helix Collector at the site receives events locally, buffers them for 1–72 hours and forwards to the centre over TLS 1.2/1.3.

Work out your price

The price follows the number of devices, the modules you choose and the licence term. Every module can be bought on its own (DLP alone, say, or SIEM alone) or together with others; choose XDR and EDR comes with it. Prices for up to 200 devices are shown here; for a larger estate a sales manager prepares an individual offer.

1. Number of devices
50 devices

Minimum order: 20 devices with SIEM, 10 devices for every other module. The volume discount does not apply to SIEM.

2. Modules
3. Licence term
Questions

Frequently Asked Questions

No. EDR shows in depth what happened on one machine, but it only sees that machine. A SIEM sees the whole estate, but only knows what the sources sent it. An attack usually leaves a trace in both: a process on the endpoint, an authentication and a connection in the estate. That is why they sit side by side in one console.

An antivirus mostly looks for the signature of a file already known to be malicious. HEDE’s pre-execution scanner reads the file’s structure instead: which combinations of calls the import table asks for, section entropy, whether the signature is genuine, and the YARA pack — and it records the evidence behind every point it awards. That is how it can judge a sample nobody has seen before, and show why it judged it that way.

No — deliberately. The endpoint module judges a file itself, on the machine; the other modules collect the events of the tools you already have, join them and raise an incident. Those tools keep doing their job, and the platform closes the gap between them.

The base distribution carries ready parsing rules for 600+ source types. For anything outside that list a decoder is written as configuration — product code is not changed and components are not rebuilt.

No. The agent is used on endpoints where it is needed; network equipment, security tools and cloud services are collected agentlessly — over Syslog, REST API, WMI, SNMP or the provider's API.

The source record is stored unmodified, a checksum is computed for each record and included in a block hash chain. Tampering or deletion is caught by scheduled background verification, and an integrity report can be produced for a period.

That depends on your event volume and retention period. Typical compression on text logs is 6–12×, and storage is split across three tiers — the expensive NVMe is only needed for hot. An exact figure follows once your stream has been measured.

An annual licence per device. The modules are independent: EPP, EDR, XDR, DLP and SIEM can be bought on their own or in any combination. If you choose XDR, EDR is not charged separately, because it is part of XDR. A volume discount applies as the device count grows, and a term discount for 2- and 3-year licences; the steps are shown in the calculator. Prices exclude VAT, which is shown on its own line.

The calculator prices up to 200 devices. For a larger estate a sales manager prepares an individual offer based on size, rollout plan and service terms. An enquiry sent from the calculator arrives with the configuration you chose.

Let's Measure Your Stream And Size The Configuration

We establish which sources, what volume and what retention you need — then give a precise proposal for components and storage.

Let’s start
Request a consultation